01 / VERIFY
Verify
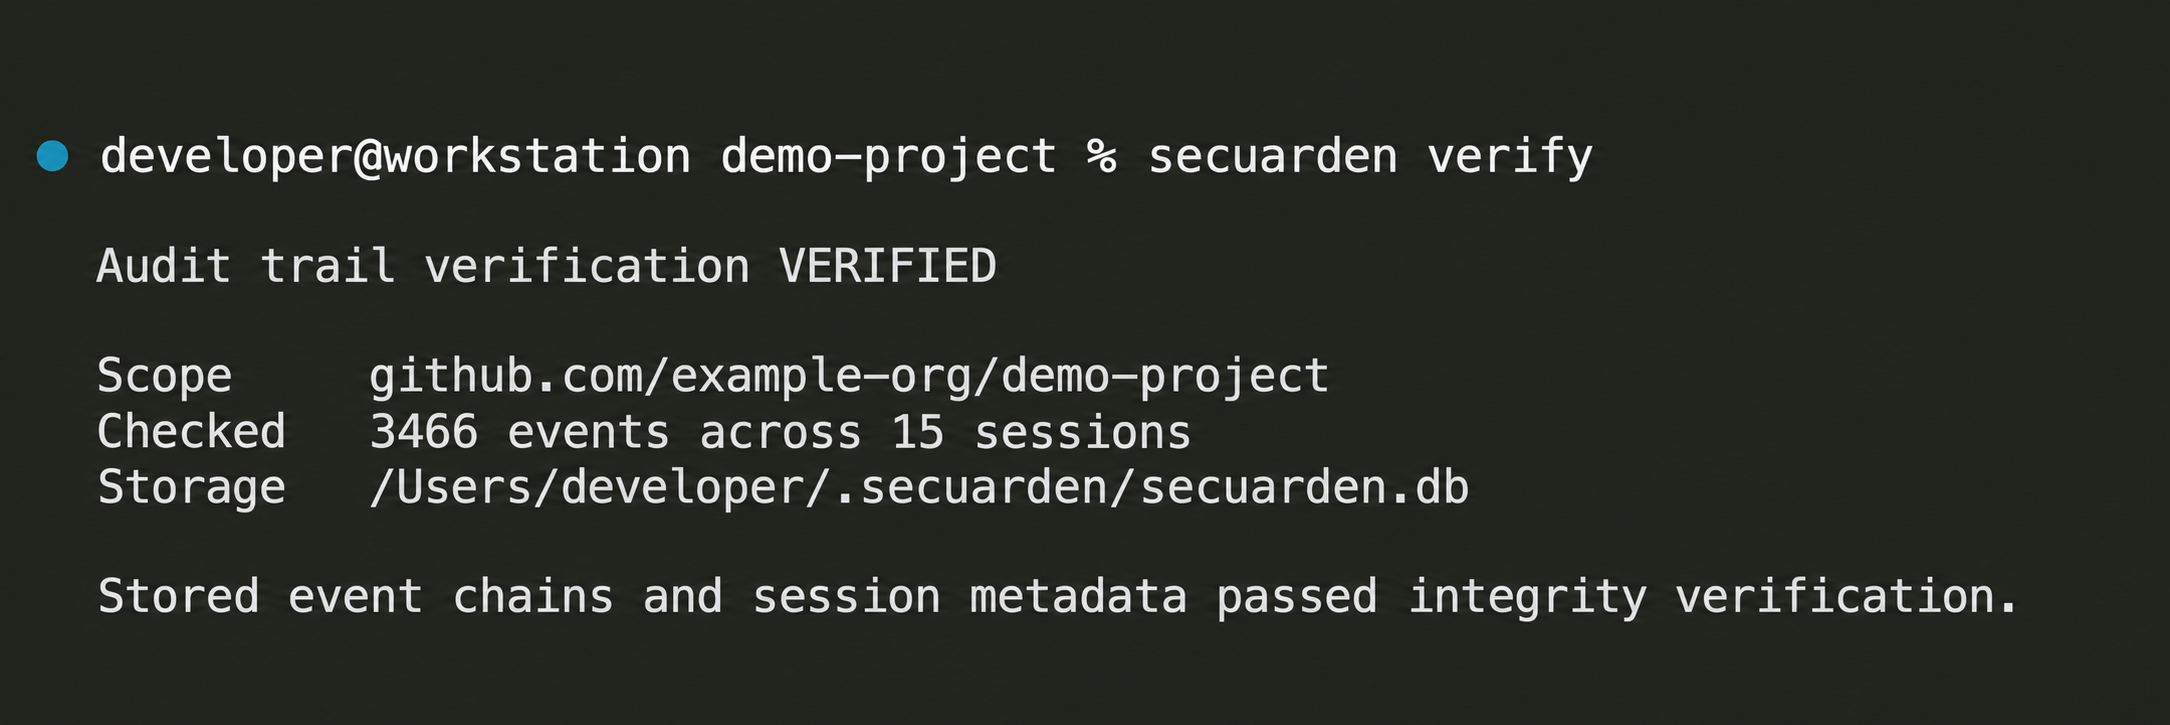
Check the integrity of captured session evidence and identify where an event chain has changed or become incomplete.
Capture supported coding-agent activity, verify evidence offline and export a Context Bill of Materials—with no source code leaving your environment. Use configurable CI thresholds to flag or fail changes based on observed risk signals.
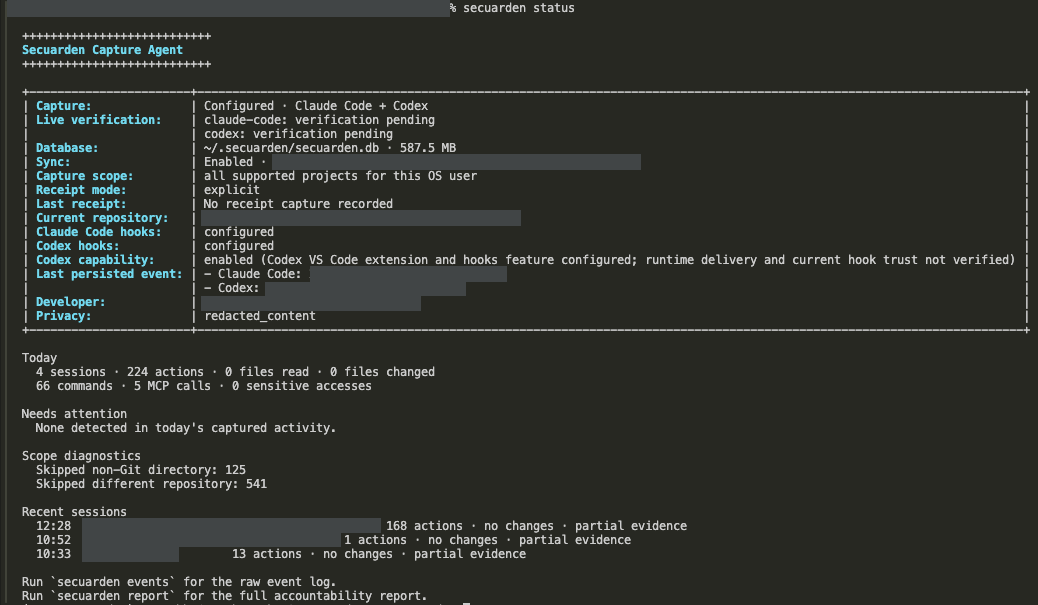
Run secuarden status to inspect configured agents, capture settings, recent activity and evidence status.
Git records the resulting code. Secuarden CLI preserves supported agent and tool activity, developer identity, repository context and resulting changes—then connects new events through a per-session SHA-256 hash chain.
Check the integrity of captured session evidence and identify where an event chain has changed or become incomplete.
Produce a portable Context Bill of Materials from the already-redacted local evidence store.
Apply configurable risk thresholds in CI and return a non-zero exit code when captured changes require intervention.
Capture activity through native hooks, including sessions, developer prompts, tool calls and results. Works with Claude Code’s official VS Code extension; Codex capture requires a compatible, enabled hook runtime.
Choose metadata-only capture to keep prompt, command, output and diff content out of the evidence store.
Export structured evidence without rereading source files or requiring a network connection.
Run configurable, deterministic risk checks in GitHub Actions, GitLab CI or any shell-based delivery pipeline. The CLI can flag or fail captured changes when they meet your selected threshold; it does not replace enterprise authorization, approval or policy enforcement.
Risk signals cover authentication, payments, secrets, cryptographic material, infrastructure, database migrations and sensitive configuration. Every result includes its contributing reasons.
Secuarden’s Policy Enforcement Engine will evaluate agent actions against repository policy, enforce permission boundaries and required approvals, and bind every allow, block and exception to the agent session and exact code change.
The CLI provides the local provenance and verification foundation for this broader assurance model.
Documentation and test changes can receive lower risk ratings. Sensitive paths can receive higher ratings with transparent reasons. Secuarden complements SAST, dependency scanning and licence analysis by preserving how an AI-assisted change was produced and evaluating the evidence surrounding it.
Existing databases upgrade automatically. Older events remain available and are clearly identified as predating hash chaining. No Secuarden account or cloud connection is required.
Follow the newest release update directly from the Secuarden team.
Read the latest Secuarden CLI release announcement from the Secuarden team.
View post on X →